ClickFix Has a Debug Mode, and the Criminals Left It On
A macOS ClickFix kit we pulled apart skips all of its own bot and admin checks if you add ?force_fake_captcha=1 to the URL. I guess even malware authors need to test their code too!
Debug Mode
Every developer has written something like this at some point:
if (new URLSearchParams(window.location.search).get("force_fake_captcha") === "1") {
    return true;
}
You add a flag so you can see the feature without jumping through all the hoops, you promise yourself you'll take it out before release, and then, oops, you forgot! It turns out criminals do this too.
The Kit
Our Threat Intelligence pipeline recently flagged a new ClickFix lure aimed at Mac users, the same campaign we wrote up in our macOS stealer analysis. It does the usual things, it shows a fake reCAPTCHA, tells you to open Terminal and paste a command to "verify you're human", and that command installs an infostealer.
The kit works quite hard to avoid being seen by the wrong people. Before it shows the lure, it checks that:
- You're on a Mac, and not an iPad pretending to be one.
- You're not a bot. It looks at
navigator.webdriverand checks the user agent for HeadlessChrome, Puppeteer, Selenium and friends. - You're not the site owner. If there's a WordPress logout link on the page, you're logged in as an admin, so it stays quiet and sets a cookie so it never shows you the lure at all.
- You haven't seen it before. That
fkrc_showncookie means each visitor only gets one go.
The point of all that is to stay hidden from researchers, scanners and the person who could actually fix the site.
The Debug Flag
Then, right at the top of the check function, before any of that:
async function shouldShow() {
    if (new URLSearchParams(window.location.search).get("force_fake_captcha") === "1") {
        return true;
    } else if (looksLikeABot()) {
        return false;
    } else if (isWordPressAdmin()) {
        setShownCookie();
        return false;
    } else {
        return !document.cookie.includes("fkrc_shown=");
    }
}
I've 'prettified' the function names because the originals are the usual _0x4f311c obfuscated ones.
Add ?force_fake_captcha=1 to the URL and the bot check, the admin check and the "already seen it" cookie are all skipped. There's a matching ?fake_captcha_lang= parameter too, so the operator can preview the lure in any of the dozen or so languages it ships with, including Arabic, Hindi, Japanese and Vietnamese. Someone clearly needed to check that the German translation looked right!
The one thing the flag doesn't skip is the Mac check, because that happens earlier, when the script decides whether to load at all. So you still need a Mac, or a Mac user agent. Here's what it looks like:
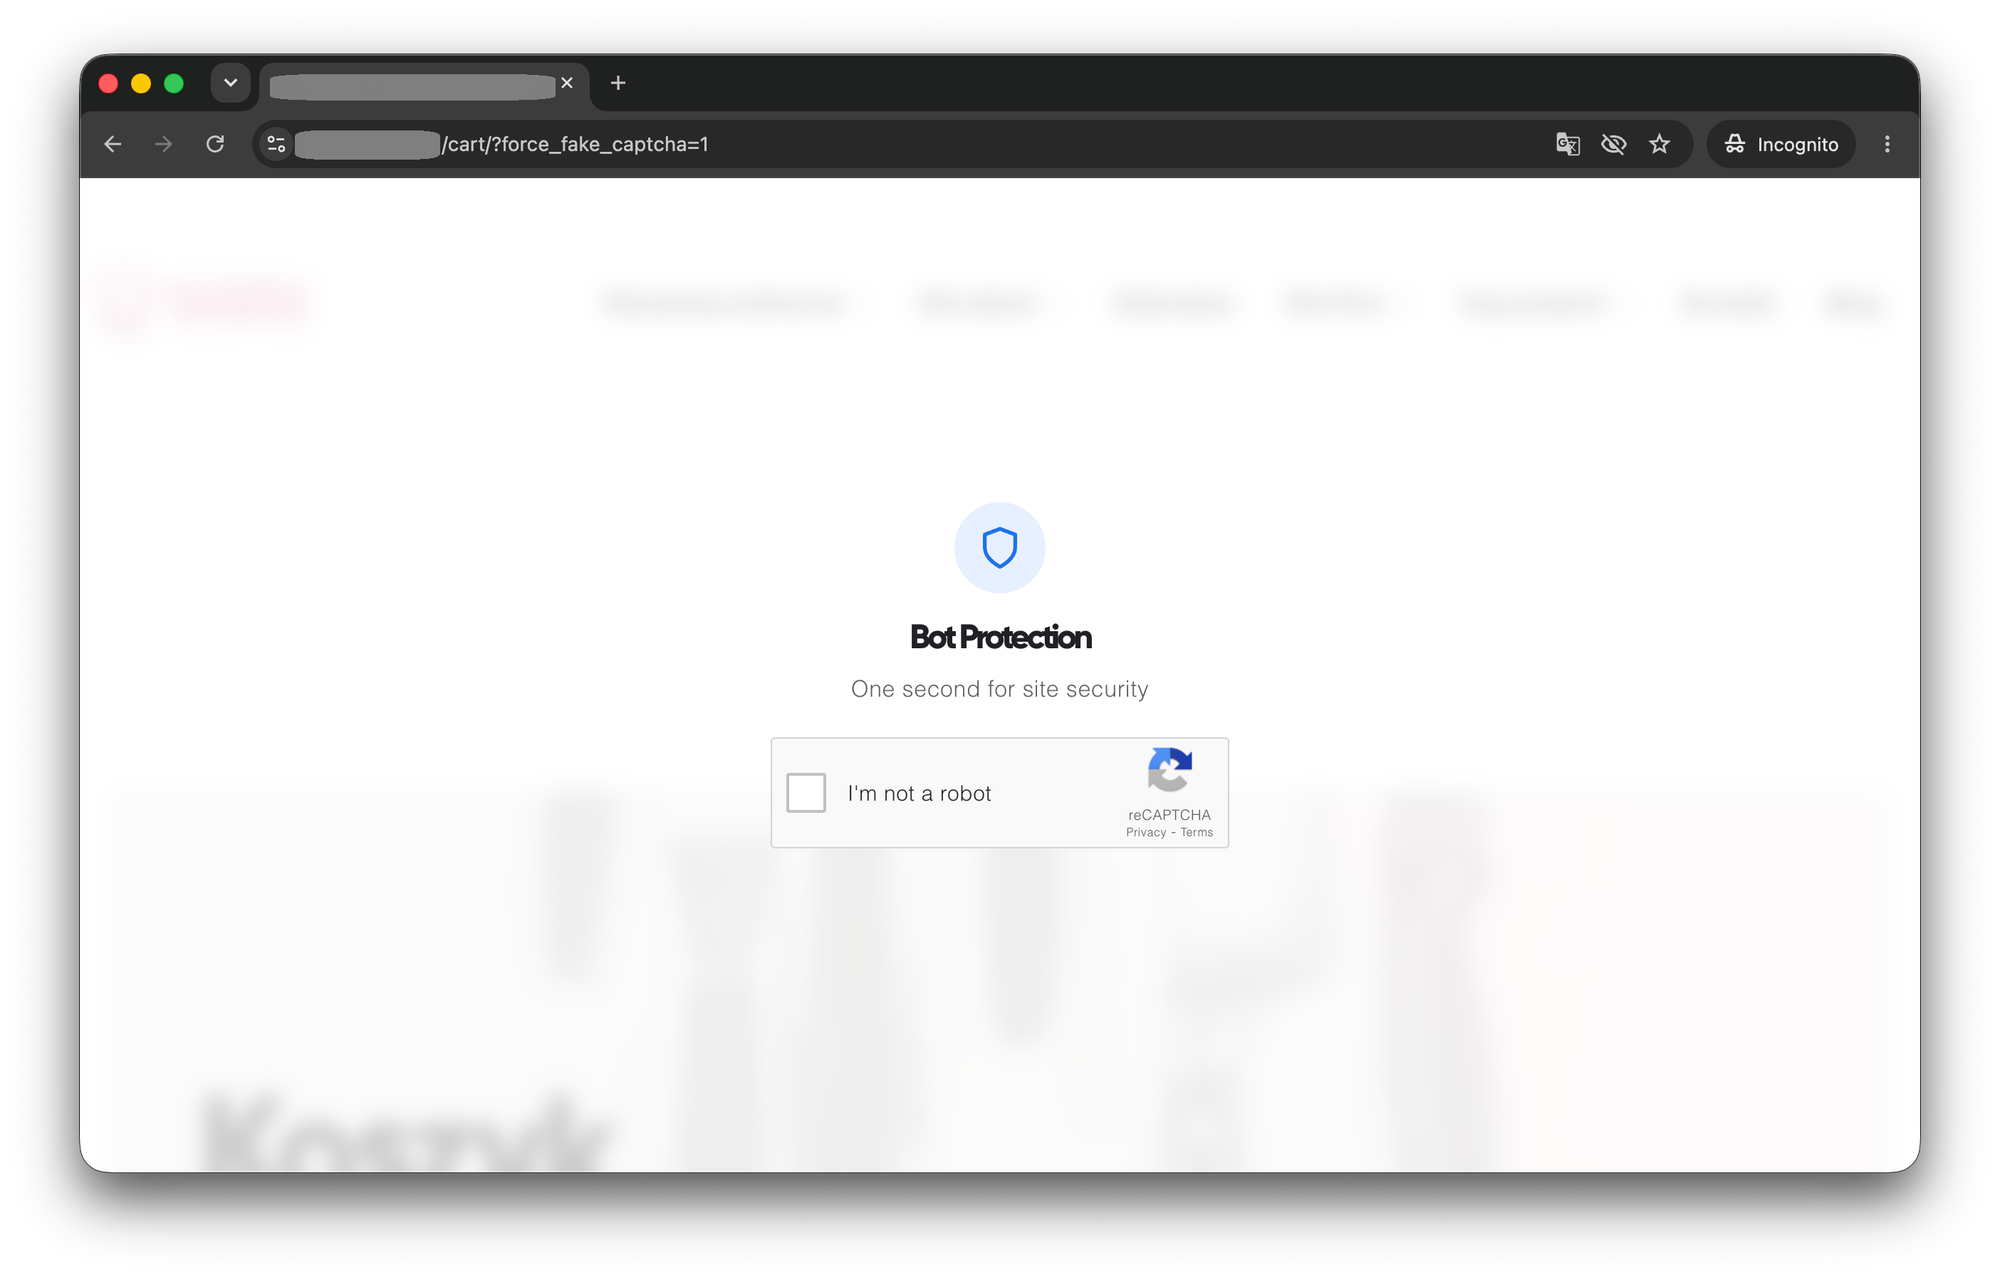
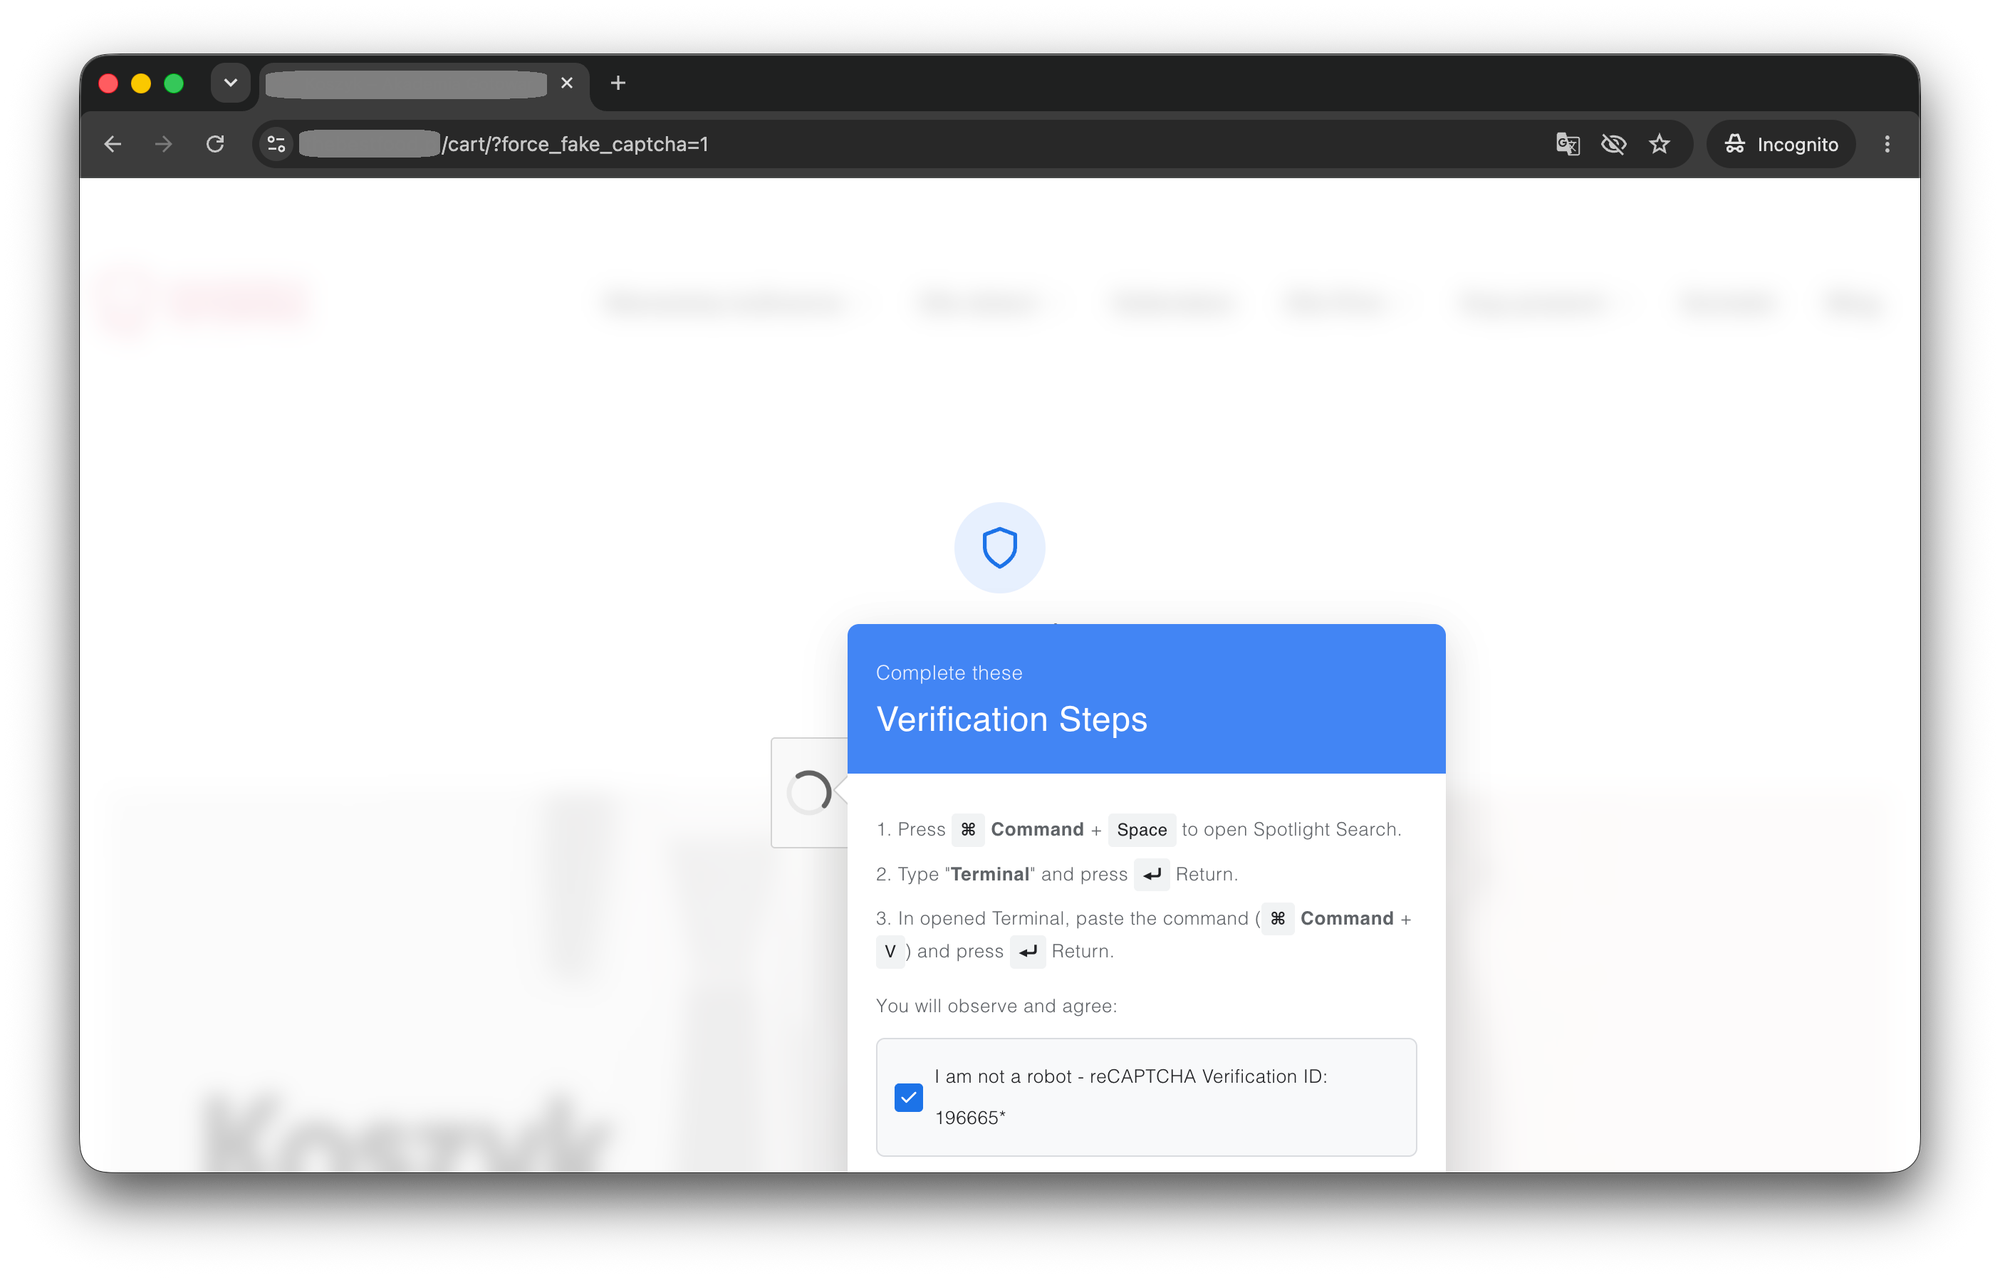
The debug flag doesn’t make the campaign any less dangerous, of course, but it does give us a rare look behind the curtain and I also found it a little entertaining. A kit built to evade researchers still shipped with a shortcut that lets us skip its checks and inspect the lure. Small oversights like this can reveal a lot about how an attack works, and help defenders spot when similar activity reaches their own sites.
If you want to see what's running on your own site, you can start a 30-day free trial with Report URI, no credit card required: Get Started Now →