A Fake Captcha, a Trojanised File Manager, and a Year of IOC C2 Domains
On 7th October our Threat Intelligence pipeline flagged a script from ohhhhhmoney.com injected into compromised WordPress sites. It is a ClickFix kit, and at the end of the chain is a backdoored copy of a real desktop app. Its Command and Control (C2) server moves to a new domain every week like clockwork. We recovered the algorithm that picks the domain, which let us list every C2 domain the campaign has used so far, and every domain it will use in the future.
The chain
Here's a high-level overview of the steps involved in the attack:
- The lure.
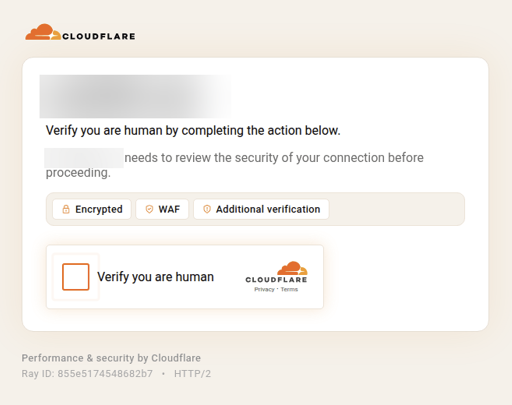
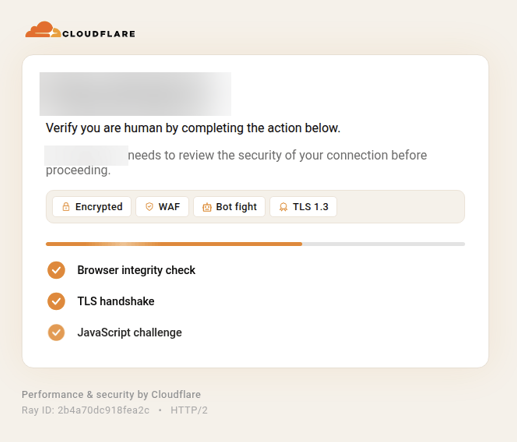
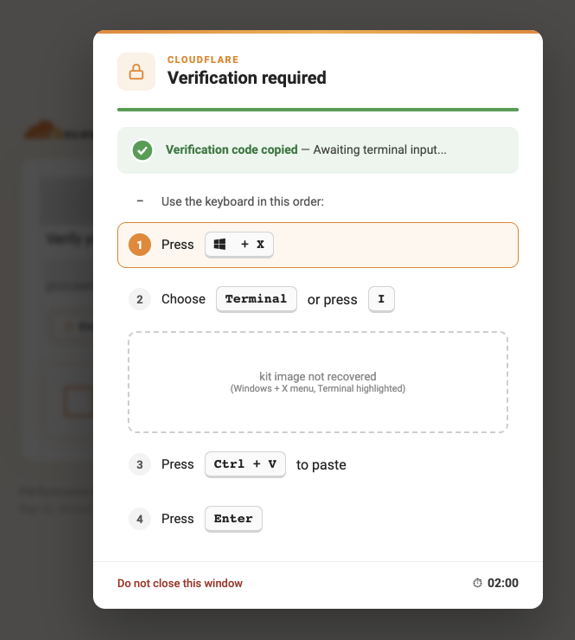
kbS0.jsfingerprints the visitor (screen size, timezone, and whether the browser is automated), then injects a full-screen iframe with a fake Cloudflare "verify you are human" page. The script suppresses the lure for visitors it identifies as bots or repeat visitors. - The clipboard. The fake check copies a PowerShell command to the clipboard and tells the visitor to paste it into the Run dialog.
- The dropper. The command hides its own window, downloads a 111 MB zip to
%TEMP%, unpacks it, and runsFileside.exe. - The disguise. The zip contains Fileside 1.9.6, a legitimate Electron file manager. Every binary is the genuine build. Only
resources/app.asar, the bundle that holds the app's JavaScript, has been rebuilt, and the victim sees a working file manager open.
The lure itself is as convincing as usual, the operators of these attacks continue to produce high quality assets. Here's what it looks like:
The backdoor
About 313 KB of obfuscated JavaScript has been prepended to the app's real main.js. It:
- registers the app to start at every login;
- stores a random victim ID in
%APPDATA%\daemons.log; - reads an affiliate tag from a
readme.txtnext to the executable, which suggests the dropper is distributed by several partners; - every three minutes, POSTs the victim ID, computer name, username and affiliate tag to
https://<C2>.com/xcv/, with TLS certificate checks turned off; - runs whatever comes back: either JavaScript executed with full Node.js access, or a bundle of files written to disk with the executable among them launched.
This code doesn't steal anything by itself, it appears to just be a foothold for additional payloads that come later, and the operator decides what to deliver through it.
The C2 domain changes every Thursday
The C2 hostname comes from a domain generation algorithm (DGA) seeded by the current week. The name changes at 00:00 UTC every Thursday, which is where Unix-epoch weeks begin. We ran the obfuscated function in isolation and set the clock to each week from October 2025 through April 2027 to extract all of the possible domains.
13 of those domains are registered, one for every week since mid-July 2026, with no gaps. Each was registered on or around the day of the Thursday it went live, across five different registrars, and each sits behind Cloudflare. None of the future names are registered yet as it seems the operator buys each domain only when it is needed.
Indicators of compromise
Delivery
| Indicator | Type |
|---|---|
ohhhhhmoney.com |
ClickFix loader, landing page and dropper host |
C2 domains (registered)
| Week from (Thu, UTC) | Domain | Registered |
|---|---|---|
| 2026-07-16 | nhyeoeaueesyih.com |
2026-07-21 |
| 2026-07-23 | srnnereaivm.com |
2026-07-23 |
| 2026-07-30 | heahnoetsteot.com |
2026-07-30 |
| 2026-08-06 | reoineueryete.com |
2026-08-06 |
| 2026-08-13 | gradnoesieheco.com |
2026-08-13 |
| 2026-08-20 | iwtuhfuei.com |
2026-08-20 |
| 2026-08-27 | dtteeoerp.com |
2026-08-27 |
| 2026-09-03 | vaituusoeeaanu.com |
2026-09-03 |
| 2026-09-10 | daihmtnawe.com |
2026-09-10 |
| 2026-09-17 | ieyoqrhtz.com |
2026-09-17 |
| 2026-09-24 | seitinloelinsa.com |
2026-09-25 |
| 2026-10-01 | chueohoe.com |
2026-10-02 |
| 2026-10-08 | teevoeeaoobn.com |
2026-10-08 |
C2 domains (to the end of 2026, not yet registered)
| Week from (Thu, UTC) | Domain |
|---|---|
| 2026-10-15 | tnseeirhenlroa.com |
| 2026-10-22 | anrwjawtraha.com |
| 2026-10-29 | nersdeoyioyrpr.com |
| 2026-11-05 | msotdticd.com |
| 2026-11-12 | hhtvotdinpeuae.com |
| 2026-11-19 | elnetbiteteho.com |
| 2026-11-26 | ocaoaooaevcian.com |
| 2026-12-03 | ehoieaeetoold.com |
| 2026-12-10 | ateieriot.com |
| 2026-12-17 | wunedazeitraie.com |
| 2026-12-24 | eueebgieae.com |
| 2026-12-31 | ouifktietaoe.com |
Unexpected connections to these domains warrant urgent investigation. A host running this backdoor should be treated as compromised because the operator can execute arbitrary code with the application’s privileges.
Where Report URI fits
The browser can catch the first step of this attack, which is a script from ohhhhhmoney.com loading on one of your pages, and that's the bit we can alert you to. ohhhhhmoney.com and all of the associated domains are now flagged in our Threat Intelligence feeds, so any Report URI customer whose site starts loading it gets the report flagged as a known Indicator of Compromise. The C2 domains above are unlikely to appear in browser telemetry, so they are here for endpoint and network defenders that may wish to use them to protect their customers.
Spot malicious scripts on your website before they put your visitors at risk, start your free Report URI trial today, with no credit card required.